Conversations
3 min read
Edera: a micro-VM and a kernel for each workload
Kavitha Daula, VP of Engineering at Edera, on why containers sharing one kernel is a risk, zones per workload, and isolation for AI-written code.
By  Luca Berton
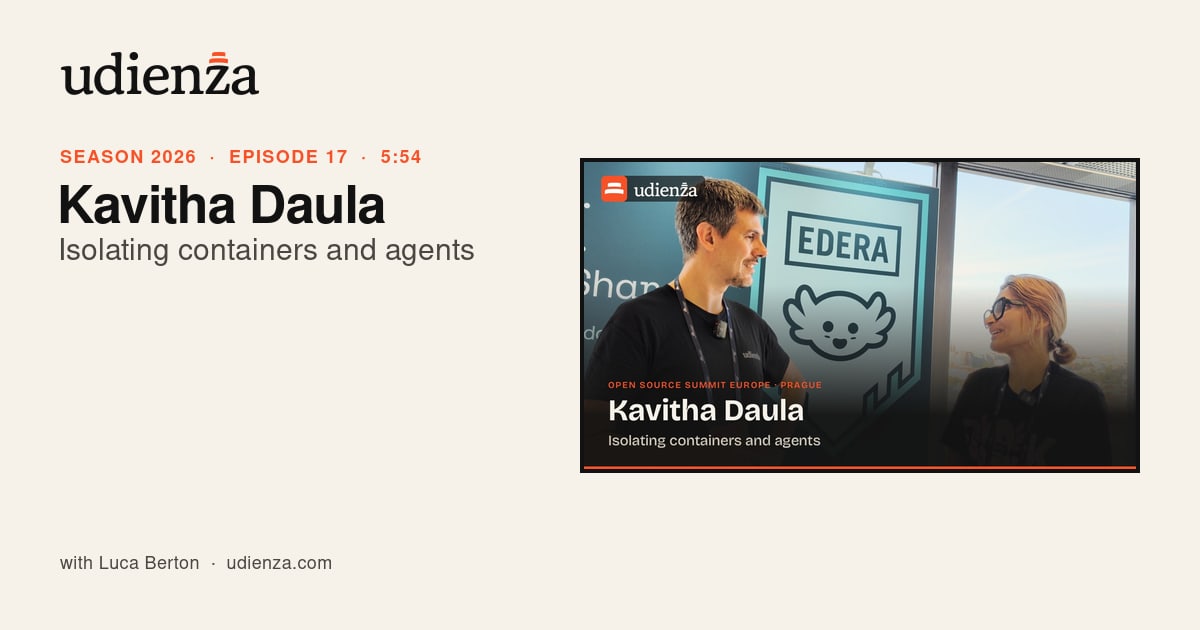
Kavitha Daula is VP of Engineering at Edera. Luca Berton talked to them at Open Source Summit Europe in Prague on 7 October 2026. Asked what Edera is, Kavitha Daula first took a step back: “before I explain what Edera is, I would love to talk about isolation in general.”
One kernel, shared
Containerized workloads run on Kubernetes, and the containers there share one single kernel. Anything that can affect the kernel can affect all of them. “And a container that’s compromised can take down the whole cluster”, because once something has access to the kernel through one container, it can pass along to the rest.
A micro-VM for each workload
Edera is building “a secure micro VM for a lot of better terms where each and every workload gets its own individual guest kernel.” Edera calls each of these a zone. If there is a breach, it happens in one particular zone and does not move across to the others, so “the amount of damage that can happen is contained to that one.”
Luca asked how a micro-VM is allocated: per tenant or per workload? Per workload, but the boundaries are the user’s to draw. “You can group multiple things into the same zone or you can have different zones with different workloads”, each of them holding together to build the architecture you would like.
Security versus performance
That freedom comes with a choice. “But then, the security versus performance challenge would always come.” Whoever designs the system has to decide how to architect it: what lives in its own zone, and what is kept separate.
Where isolation is used
The first use case Kavitha Daula named is the highly regulated environment, where you do not want hostile multi-tenant workloads in the same cluster. “You don’t want to have CI and database and everything running together in the same thing”, when each of them can be in its own separate zone. Healthcare and banking are the sectors they pointed to.
The second is AI workloads, especially in this time of AI agents, and they referred to an incident involving AI agents to make the point. Still, they do not see isolation as a problem of regulated environments only. “Anybody who’s using Kubernetes should be looking at isolation pretty seriously”, and now that extends to everybody who is using AI in some way or the other.
AI-written code adds to the risk. “And if the code is getting written by AI, what should be written in five lines is now 50 lines.” Over time, nobody knows everything that is in there, or what can be impacted.
What comes next
“Every day is a learning experience,” Kavitha Daula said. Last year, the interesting part for them was getting Edera to work at scale in a way that is both performant and secure. Now the team is trying to make Edera run on different kinds of things, past Kubernetes.
What they love most personally is educating people on the challenges with Kubernetes itself, and on “the security concerns of running things on a vanilla container.” Bringing people that awareness is what they find important. Luca added that Kubernetes might differ from one of the many flavours on the market to the next.
To try it, they pointed to the website, on.edera.dev, where at least one node of Edera can be spun up to play with.
More
The episode with Kavitha Daula: Isolating containers and agents. The week it was recorded: Open Source Summit Europe 2026: who we met.
Questions and answers
Is an Edera micro-VM allocated per tenant or per workload?
Per workload, Kavitha Daula said, but the user decides: several things can be grouped into the same zone, or different workloads can sit in different zones.
Where is Edera's isolation used?
In highly regulated environments such as healthcare and banking, where hostile multi-tenant workloads should not share a cluster, and for AI workloads and agents.
How can Edera be tried?
Through the website on.edera.dev, where at least one node of Edera can be spun up to play with.
Built something the rest of us run on? Being a guest is free. Take the other chair
Related articles
All articles →-
Conversations · 2 min read
Aikido Security: toward self-securing software
What Aikido Security builds, as Xander Van Buggenhout told it in Utrecht: code-to-cloud scanning, AI pentesting, device protection and autofix.
-
Conversations · 1 min read
Reviving Cluster API for Talos Linux
Pepijn Oomen of Redpill Linpro asks the community to take over the Cluster API control plane and bootstrap providers for Talos Linux, marked deprecated.
-
Conversations · 2 min read
Isovalent: private networks for VMs on Kubernetes
A VPC for your Kubernetes cluster: Isovalent Private Networks gives VMs sticky IPs and their own subnets on KubeVirt, as Raymond de Jong explained at TalosCon.
The episodes in this article
All episodes →-
Episode 17 · 10 Nov
Kavitha Daula: Isolating containers and agents